LiteLLM supply chain attack: attackers distribute credential-stealing malware through a compromised release
23 Oct 2026
On 21 October 2026, LiteLLM disclosed a compromise of its release pipeline that involved distribution of a malicious version LiteLLM 1.107.0 that contained malware which was designed to steal credentials and allow attackers to execute arbitrary code remotely.
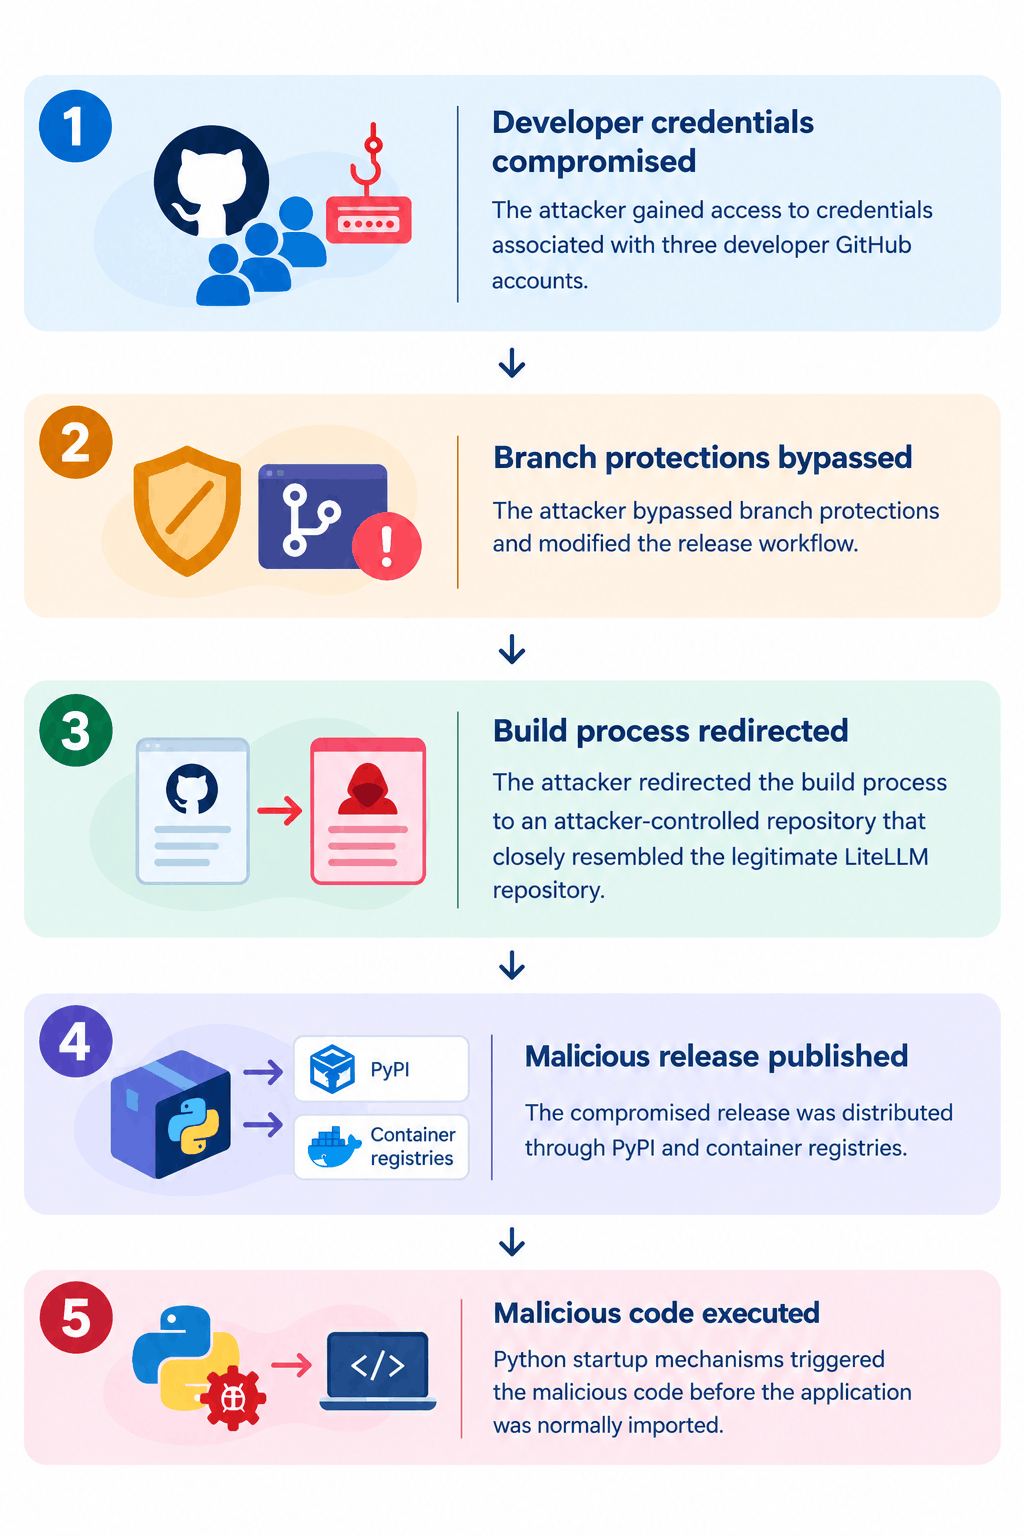
According to LiteLLM, the attacker used compromised developer GitHub credentials to modify the release workflow and publish a malicious version that was built from an attacker-controlled repository.
Through our blog, we will understand the LiteLLM supply chain attack, its potential impact on organizations, and what they can do to defend.
About the threat
|
Threat name |
Attack type |
Affected component |
Affected version |
Initial disclosure |
Status |
|
LiteLLM Supply Chain compromise |
Software Supply Chain Compromise / Credential Theft
|
LiteLLM Python package and container images
|
LiteLLM 1.107.0
|
21 October 2026
|
Compromised artifacts removed. Investigation ongoing. |
The affected artifacts, as confirmed by LiteLLM, are:
- PyPI: LiteLLM 1.107.0, including all seven published wheels. The compromised packages were available from 11:39 UTC to 13:23 UTC on 21 October 2026.
- Docker Hub: The tags v1.107.0, latest, main-latest, and main-stable pointed to compromised images from 11:46 UTC to 14:20 UTC.
- GitHub Container Registry (GHCR): The tags v1.107.0, latest, main-latest, and main-stable were also affected during the reported incident window.
The company has advised organizations that have installed the affected package or run the compromised container during the exposure window to assume compromise of the environment.
How could it impact organizations?
An attacker can use the malicious release to:
- Steal cloud credentials, access tokens, and private keys.
- Collect developer credentials and authentication files.
- Access browser data and credentials associated with AI development tools.
- Collect environment variables and secrets available to the affected process.
- Extract credentials and configuration information from LiteLLM proxy deployments.
- Establish background execution that retrieves and executes additional code.
SharkStriker’s recommendations
- Identify all systems, development environments, and containers that installed or executed LiteLLM 1.107.0 during the reported exposure window.
- Rebuild affected virtual environments and container images from verified clean artifacts.
- Follow LiteLLM’s official remediation instructions before restarting Python processes in affected environments.
- Rotate potentially exposed cloud credentials, provider API keys, LiteLLM master and virtual keys, database passwords, and other secrets accessible to affected systems.
- Review cloud audit logs for suspicious credential usage, including AWS CloudTrail events where applicable.
- Inspect GitHub audit logs and CI/CD workflows for unauthorized modifications or suspicious release activity.
- Pin dependencies to verified versions and use immutable artifact digests where supported.
- Strengthen release-pipeline controls, credential protection, and artifact verification to reduce the risk of similar supply chain compromises.
SharkStriker’s Actions:
- Threat intelligence reviewed using LiteLLM’s official incident report and supporting security research.
- The affected package version, container tags, and reported exposure windows documented.
- Credential theft and compromised software distribution identified as priority investigation areas.
- Detection engineering recommended to review Python startup behavior, suspicious outbound connections, and unauthorized CI/CD activity.
- Threat hunting recommended for potentially affected development systems, containers, and cloud environments.