BigDiskBuster: PoC for a Microsoft Defender Update DoS technique
21 Sep 2026
A security researcher named Nightmare Eclipse released a PoC named BigDiskBuster on GitHub, demonstrating a technique that can be used to interfere with the Microsoft Defender platform and its security intelligence updates.
Let us understand the technique, the threat it poses, and what organizations can do to defend against it.
About the vulnerabilities
|
Threat name |
Vendor + Component impacted |
Threat type |
When was it discovered? |
About the technique |
|
BigDiskBuster – Microsoft Update Interference PoC |
Microsoft Windows + Microsoft Defender Antivirus |
Defense evasion/ Security update DoS technique |
September 2026 |
If successfully executed, it can prevent Microsoft Defender from receiving updates and leave the endpoint with outdated protection. |
This PoC was identified by the SOC team as part of an ongoing threat intelligence and security monitoring activity.
What can attackers do with the technique?
This technique can be used by attackers to:
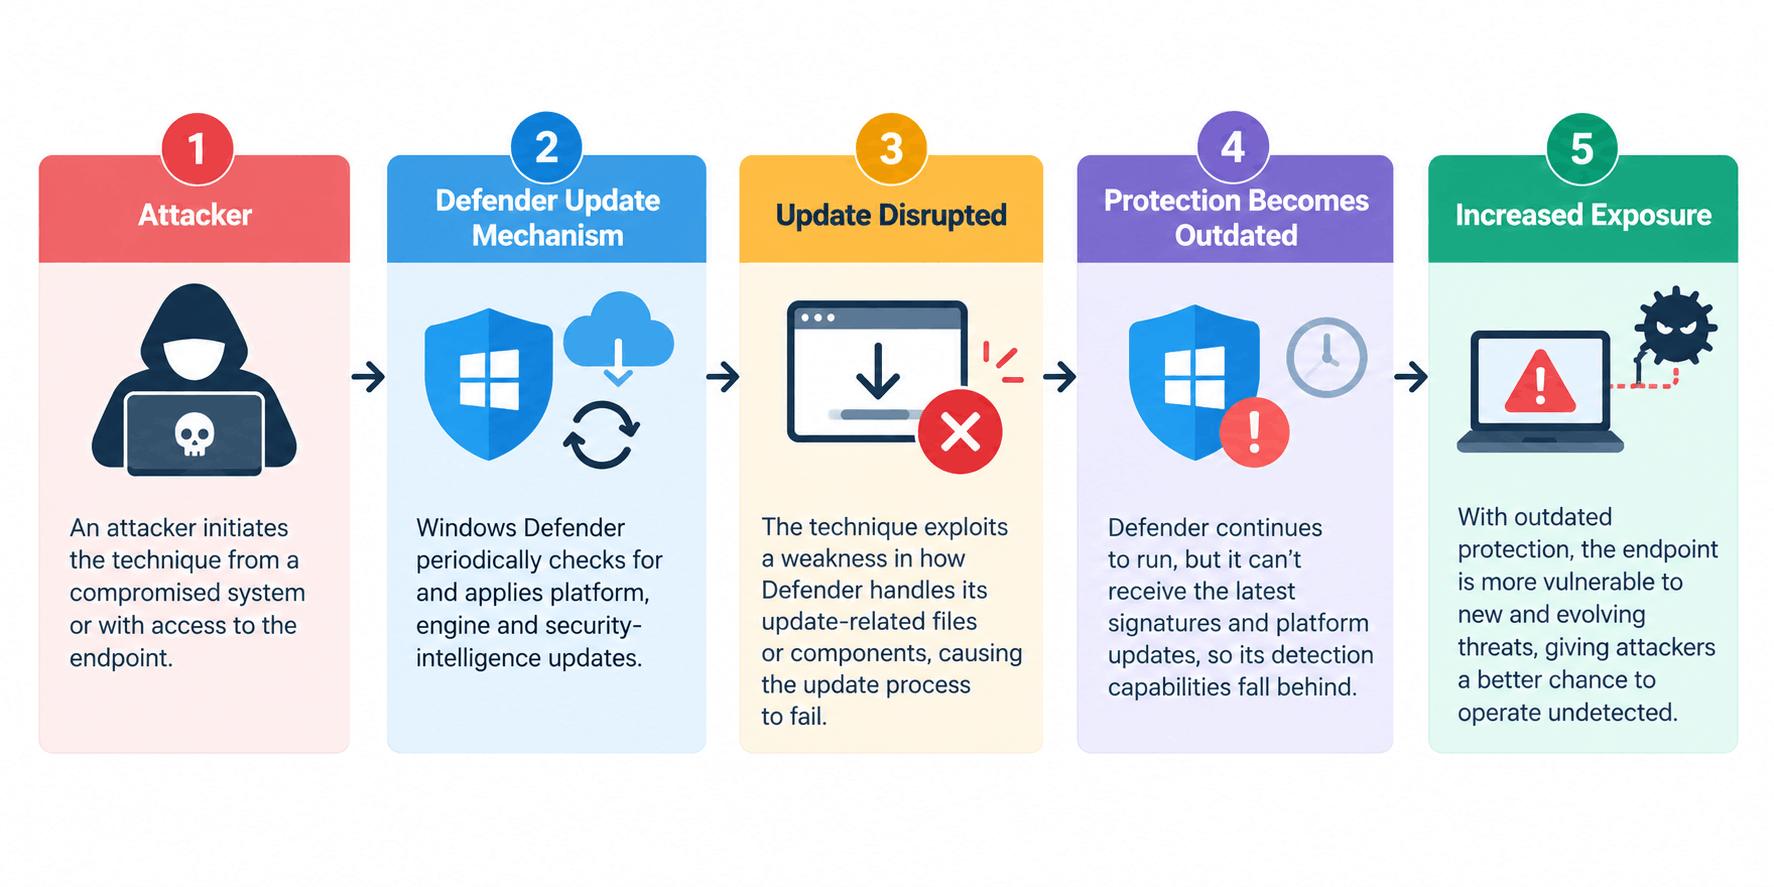
- Disrupt Microsoft Defender security intelligence or platform updates.
- Leave endpoints with outdated detection capabilities.
- Reduce protection against newly identified malware.
- Help attackers evade endpoint security controls.
Official security guidance
Organizations should ensure that Microsoft Defender Antivirus remains enabled and receives regular security intelligence and platform updates.
SharkStriker’s actions
- Ensure Microsoft Defender Antivirus and security intelligence updates are enabled and up to date.
- Restrict unnecessary administrative privileges.
- Ensure EDR/XDR protection remains enabled.
- Actively monitor the environment for attempts to interfere with Microsoft Defender updates or protection mechanisms.