Rapuncel Infostealer – a newly identified infostealer that disables 145 security processes
22 Sep 2026
Security researchers have identified a new infostealer titled Rapuncel that steals sensitive information by disabling security tools through the abuse of a Microsoft-signed Windows kernel driver.
Through the blog, we will understand what the infostealer is about, the threat it poses, and what organizations can do to defend against it.
About the vulnerabilities
|
Threat name |
Vendor + Component impacted |
Threat type |
Technique used |
|
Rapuncel/BYOVD |
Microsoft Windows/Windows kernel |
Infostealer |
BYOVD (Bring Your Own Vulnerable Driver) |
Here is what happens:
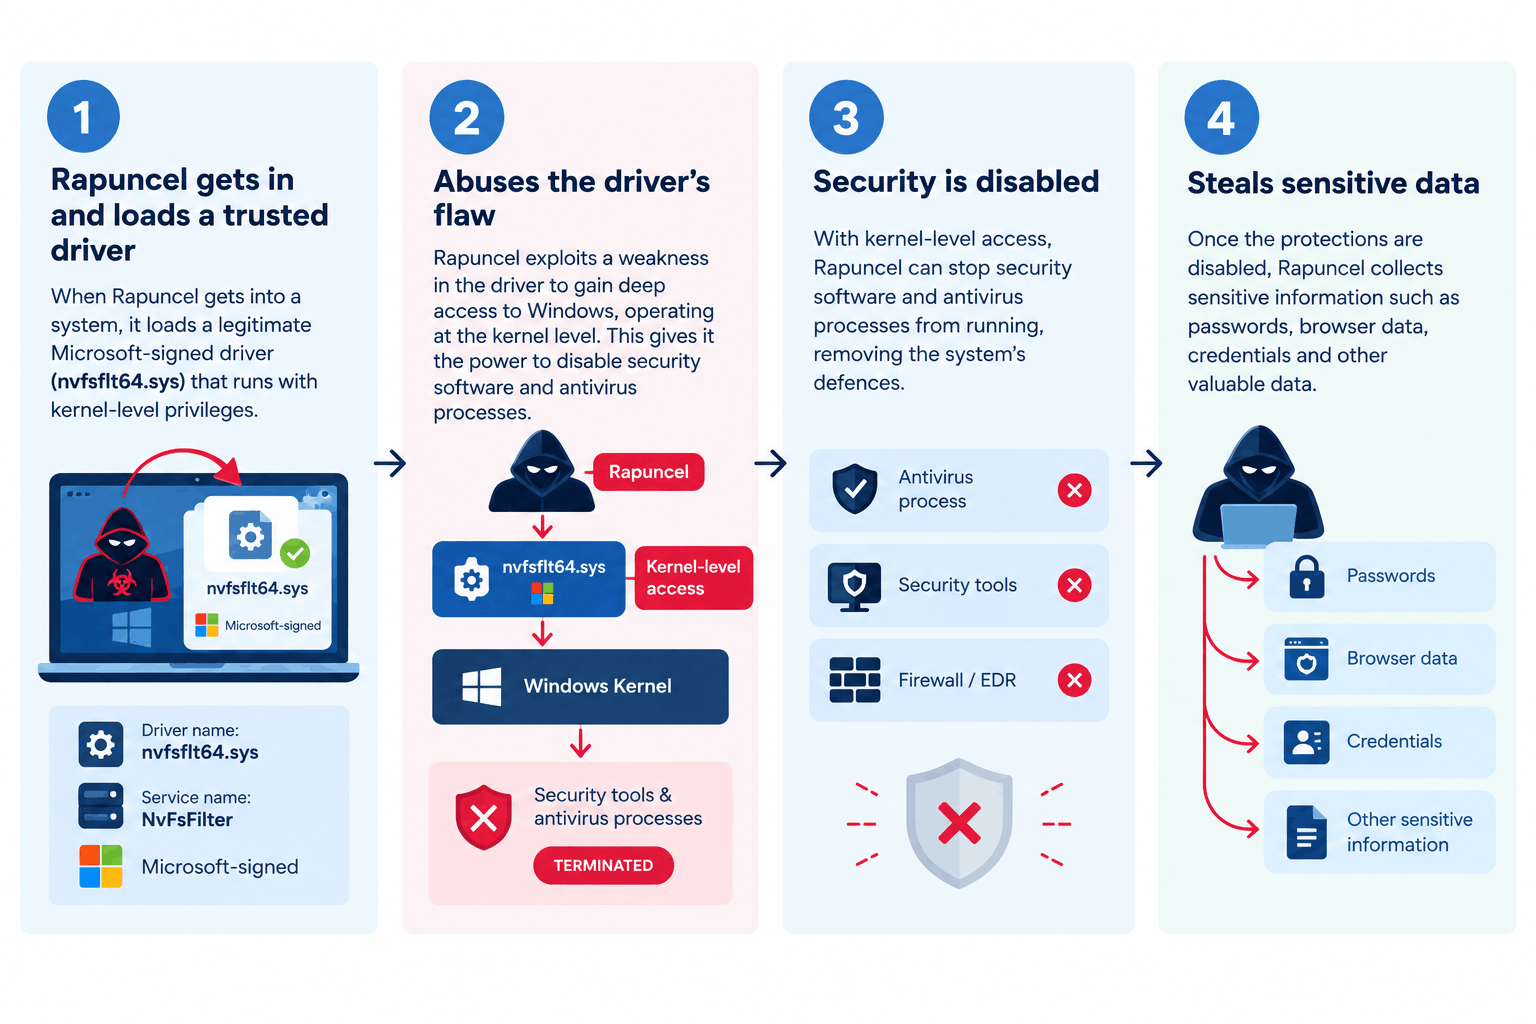
When Rapuncel gets into a system, it loads a legitimate Microsoft-signed driver (nvfsflt64.sys) that runs with kernel-level privileges. It abuses the flaw in the driver to gain deep access in Windows to disable security software and antivirus processes.
Once security measures are disabled, it starts stealing sensitive data – passwords, browser data, credentials, and other sensitive information.
What is the threat posed by the infostealer?
Attackers can use the infostealer to:
- Disable or terminate antivirus and EDR security processes.
- Reduce endpoint security and detection capabilities.
- Steal browser credentials, cryptocurrency wallet information, and other sensitive data.
- Maintain malicious activity with reduced visibility from security controls.
SharkStriker’s recommendations
- Enable Microsoft Defender Vulnerable Driver Blocklist and ensure it is regularly updated across supported Windows endpoints.
- Enable Memory Integrity (HVCI) to prevent untrusted or vulnerable drivers from loading into the Windows kernel.
- Restrict driver installation privileges to authorized administrators only.
- Use application allowlisting to prevent unauthorized executables and driver installers from running.
- Keep Windows fully updated with the latest security patches.