CVE-2026-35273: An actively exploited critical RCE flaw in Oracle PeopleSoft Enterprise PeopleTools
23 Sep 2026
Security researchers have reported an actively exploited critical vulnerability affecting Oracle PeopleSoft PeopleTools and PeopleSoft Enterprise.
In this blog, we will understand what the flaw (CVE-2026-35273) is about, the threat it poses, and what organizations can do to defend against it.
About the vulnerabilities
|
Vendor/ Component impacted |
Threat Type |
CVE identifier/ |
Affected components |
Affected versions |
|
Oracle Corporation + PeopleSoft PeopleTools |
Remote Code Execution |
CVE-2026-91843/ 9.8 |
Updates Environment Management / Environment Management Hub (EMHub) |
– Oracle PeopleSoft Enterprise PeopleTools 8.61 |
|
Threat actor |
Exploitation status |
Attack vector |
|
UNC6240/ShinyHunters |
Actively exploited as zero-day |
Network/HTTP |
The flaw was initially disclosed on June 10, 2026, after Google Threat Intelligence reported exploitation between May 27 and June 9, 2026, as a zero-day.
ShinyHunters’ recent claim of compromising FBI systems through the exploitation of the flaw has raised concerns about continued risk to organizations running internet-facing Oracle PeopleSoft environments.
Threat posed by the vulnerability
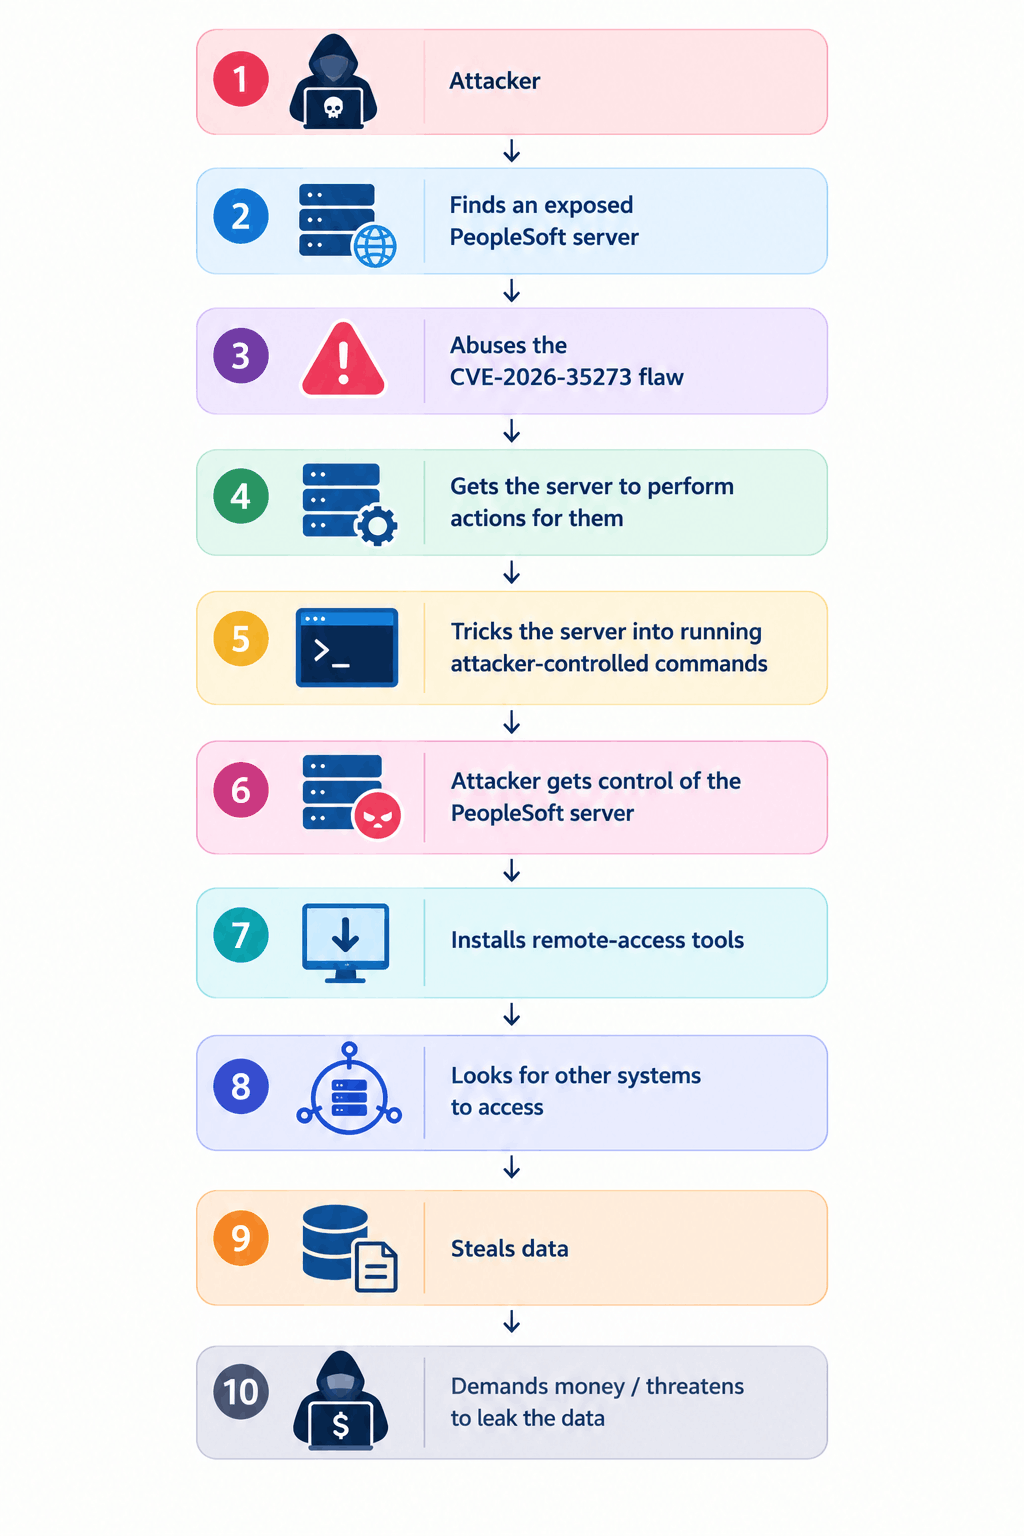
By successfully exploiting the vulnerability, an attacker can:
- Execute arbitrary code on the affected PeopleSoft server.
- Take control of the PeopleSoft environment.
- Establish persistence on compromised servers.
- Conduct reconnaissance of internal systems and configurations.
- Move laterally to other systems within the organization’s environment.
- Access and potentially exfiltrate sensitive business, employee, financial, or student information.
- Deploy additional tooling or malicious files on compromised PeopleSoft infrastructure.
SharkStriker’s recommendations
- Apply Oracle’s security fix for CVE-2026-35273 immediately.
- If patching cannot be performed immediately, follow Oracle’s mitigation guidance and disable the Environment Management Hub (EMHub) service where possible.
- For single-server configurations, consider removing the PSEMHUB application as recommended by Oracle.
- If EMHub cannot be disabled, restrict external access to /PSEMHUB/* and /PSIGW/HttpListeningConnector at the firewall or network perimeter.
- Review PeopleSoft/PIA WebLogic access logs for suspicious external requests, particularly POST requests to /PSEMHUB/hub and /PSIGW/HttpListeningConnector.
- Review the PeopleSoft web-tier filesystem for unexpected .jsp files and suspicious files or directories within the PSEMHUB application paths.
- Monitor outbound network connections originating from PeopleSoft servers for unusual or unauthorized destinations.
- Review authentication and system activity for signs of lateral movement or unauthorized administrative access.
- Ensure PeopleSoft systems are running supported versions and apply Oracle Critical Patch Updates and Security Alerts without delay.
- If indicators of compromise are identified, immediately initiate incident response and investigate the affected PeopleSoft environment for potential data access or exfiltration.